
Close What's Openon Vanta.
Embedded remediation for the document tests, cloud controls, and evidence discipline that turn a SOC 2 Type II program into an audit-ready posture.
DevBrother embeds a hands-on SOC 2 / Vanta remediation lead into your compliance and engineering workflow: from open-test inventory (or Vanta onboarding from zero) through evidence uploads, justified N/As, and safe AWS/GitHub fixes.
- Hands-on Vanta + SOC 2 Type II delivery
- Embedded with compliance + engineering
- Document evidence, automations, governance
- Audit-ready package without fake history
We've closed real SOC 2 Type II programs on Vanta. Now we're bringing that method to more organizations.
Proven Experience Closing SOC 2 on Vanta
Remediation Engineering Inside Your SOC 2 Program
DevBrother has hands-on experience driving SOC 2 Type II remediation on Vanta for a technology client, working as an embedded extension of their compliance and engineering owners, not as a slide-deck consultancy.
Vanta is the control plane. DevBrother closes what blocks the audit.
On a recent Security TSC / Type II engagement, a large open document and automation backlog was reduced to a short residual list owned by the client, with policies packaged for annual review and a non-technical maintenance guide.
Anonymized by design. We prove capability without exposing the companies that trust us with their systems, evidence, and audit timeline.
Document Evidence
Policies, access reviews, network diagrams, monitoring screenshots, CI/CD proof, HR/legal samples, and justified N/A packages, framed correctly for Type II.
Cloud & GitHub Remediation
CloudTrail, GuardDuty, VPC flow logs, IAM hygiene, S3 hardening, RDS monitoring, branch protection / rulesets, changed only with client approval.
Governance & Risk
Policy review cycles, risk treatment plans, annual risk snapshots shared with the auditor when required.
Embedded Delivery
Same Slack channel, same tracker, same accountability as your internal owners, with a clear change-control gate on production.
What We Deliver
What We Close on Vanta
The remediation layer around your SOC 2 Type II program, owned end to end by an embedded lead who cares about auditor-readable evidence, not green checkboxes alone.
Document Tests
Auditor-readable evidence packages for the document backlog that never closes itself.
Automated / Integration Tests
Cloud, identity, and GitHub controls wired through Vanta integrations, closed with real configuration, not screenshots alone.
Governance Modules
The policy and risk layers that keep Type II sustainable after fieldwork.
Platform Onboarding (when needed)
Stand up Vanta and integrations until a real test backlog exists, then run the same remediation cycle.
We don't stop at “tests created.” We close them with evidence an auditor can trust.
From open tests to auditor-readable evidence
Two Ways In
Already on Vanta or Just Want SOC 2
Same method. Different starting week.
Already on Vanta
You're subscribed, scope is set, tests are failing or “Needs remediation.” We inventory the open backlog and burn it down.
Starting from Zero
You need SOC 2 and may not know Vanta yet. We explain the stack (platform + remediation + independent CPA auditor), help onboard Vanta, pick Type II scope, connect integrations, then run the same remediation cycle.
How Vanta Fits
After you choose SOC 2 Type II and Trust Services Criteria, Vanta generates controls and tests. Integrations turn many automated checks green or red. Document tests do not close themselves. That is our work. The SOC 2 report comes from a CPA firm, not from the platform.
What We Don't Replace
We are not your auditor, not Vanta itself, and not a substitute for legal counsel or a formal penetration test (unless scoped separately). Platform subscription and auditor fees stay separate line items.
Platform creates the tests. We close them. The auditor issues the report.
How We Work
SOC 2 Remediation, Embedded Into Your Team
We work within your compliance and engineering workflows rather than behind a traditional consulting layer.
Scope
Confirm Type II, Trust Services Criteria, observation window, and owners (compliance + engineering).
Inventory
Map every open document and automated test in Vanta (or stand up Vanta first if you're Path B).
Triage
Quick wins, justified N/As, Type II templates with honest non-occurrence language where no event has occurred yet.
Remediate
Approved AWS/GitHub batches, real dated evidence, timestamps where auditors expect them, with no silent production changes.
Freeze & Handoff
Evidence freeze before fieldwork, risk snapshot, catalogued package, and a non-technical guide so your team can maintain it.
We Embed. We Close. We Hand Off.
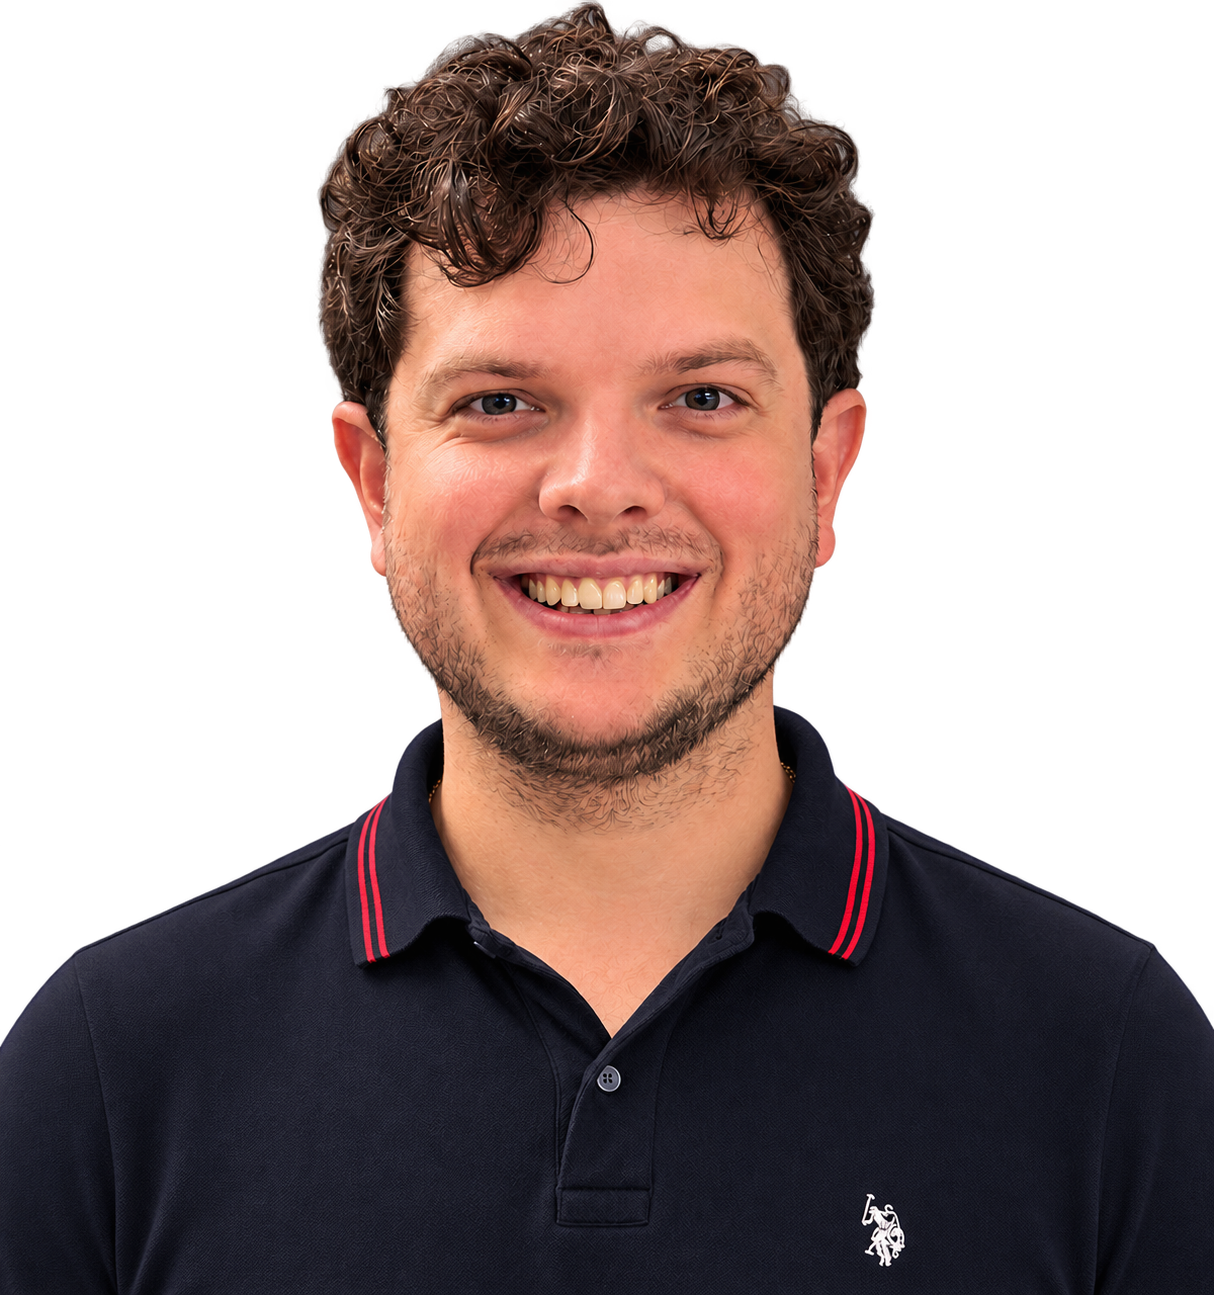
Oleksandr Melnychenko
SOC 2 Remediation Specialist
Oleksandr leads hands-on SOC 2 Type II remediation on Vanta. He works inside your compliance and engineering workflows to burn down open tests, package auditor-readable evidence, and hand off a program your team can maintain.
- Vanta SOC 2 Type II burn-down
- Document and automation evidence
- AWS and GitHub remediation
- Audit-ready package and handoff
What You Get on the Engagement
The Capability We Embed Into a SOC 2 Program
Why DevBrother
What Makes This Different
Engineering-led SOC 2 remediation, delivered through the same embedded model we use everywhere.
Embedded, Not Outsourced
Same channel, same owners, same accountability as an internal remediation lead.
Type II Evidence Discipline
Real events inside the observation window, or approved templates plus an explicit non-occurrence statement. No fabricated history.
Production-Safe Fixes
Cloud and GitHub changes only with written approval. We don't “just flip” IAM, RDS, or DNS.
Confidentiality by Default
We prove outcomes without naming clients or exposing their audit packages.
Outcome-Based Delivery
Success = closed tests, uploaded evidence, justified N/As, and a handoff your team can run, not slides.
Full Stack Around the Control Plane
Documents, automations, and governance in one engagement, not a gap list left for your two engineers to decode.
BUILD WITH DEVBROTHER